Zero Trust Basics for Complex Modern Systems - Rob Allen - ASW #409
66 min
Listen through the publisher, then discuss the episode here or arrange an in-person Roundtable. Your city determines where to meet.
Roundtables are designed for groups of four, with a shared subject and room for everyone to speak. Come for discussion, with no dating expectation.
Orgs don't have to wait for the next zero-day, the next batch of 1,000 CVEs, or the next exploit in the wild to harden their defenses. Rob Allen talks about turning an expectation of "assume breach" into proactive defenses based on zero trust. We also discuss why "assume breach" doesn't have to be a pessimistic stance or even one that presumes malicious intent. After all, with so many agents being adopted throughout an org, restricting access and adding observability reduces the side-effects of agents taking actions you didn't expect regardless of what they were prompted to do. This segment is sponsored by ThreatLocker. Visit https://securityweekly.com/threatlocker to learn more about them! Visit https://www.securityweekly.com/asw for all the latest episodes! Show Notes: https://securityweekly.com/asw-409
Episode information is provided by the publisher. Listening takes place on the publisher’s service.
The world appears to be falling apart, and the Trawl ladies are beginning to wonder whether anyone is actually in charge. From America's air traffic control system grinding to a halt, banking glitches and our ever-growing dependence on technology, Jemma and Marina are asking what happens when the infrastructure we rely on is run by systems, and people, we can't trust. Trump's America is proving quite the masterclass in chaos. There's Transportation Secretary Sean Duffy, whose career has taken him from reality TV to running America's transport network; questions over the new AI technology, the FAA's failures and the government's handling of the crisis; and another extraordinary display of Trump's blame-shifting when things go wrong. We also look at Markwayne Mullin's rather unfortunate timing when it comes to a trip to a college football game, the questions surrounding donations to Trump's enormous new ballroom and the companies subsequently winning government contracts. Are these isola
This week on the Mark Levin Show, 2028 Republican Presidential candidates must directly address the urgent threats to the country - Marxism and Islamism. These candidates should deliver bold, courageous speeches that clearly explain what is happening in the country, identify those responsible, and directly challenge these threats rather than leaving such warnings to a small number of media voices. Also, it is difficult to believe so many major outages affecting entities such as the NSA, FAA, airline systems, Microsoft, and Apple services could be merely coincidental. The timing and scale of the incidents are troubling and remain inadequately explained. President Trump had proposed a major modernization and restructuring of air traffic control in 2017 that Congress failed to enact. Had those reforms been adopted, many current FAA failures might have been avoided. Later, does Senator John Kennedy know anything about originalism? Originalism is not pure textualism. The meaning and intent
Dinosaurs were not like I thought... Check out https://groundnews.com/Cleo for a data-driven, balanced approach to staying informed. Use my link to save 50 percent on the Vantage plan and see how current events are framed from every perspective. I’m finally learning the truth about dinosaurs. I’ve loved dinosaurs since I was a kid, but it turns out a lot of what I thought I knew is wrong… or at the least outdated. So, in this video, I’m gonna show you the cutting edge of dinosaur discovery. I’ll give you rare access into a warehouse full of dinosaur bones, try to find my own fossil, and show you something new these scientists just discovered… Chapters: 00:00 What were dinosaurs really like? 01:08 Why is today a big deal for dinosaur discovery? 03:31 How big were dinosaurs, really? 05:49 When did dinosaurs actually live? 08:20 How many dinosaurs have we found? 09:26 What was the T-Rex like? 10:39 Did I find a bone?? 11:55 What IS a dinosaur? 14:31 What did dinosaur skin feel like? 15:06
Matthew Farwell’s conviction settled the federal case against him. It did not settle what may have happened to evidence, what other officers knew, or how many cases depended on his work as a Stoughton police detective. Tony Brueski is joined by retired FBI agents Jennifer Coffindaffer and Robin Dreeke to connect two questions that belong together: could there be more arrests in the Sandra Birchmore case, and should prosecutors review the cases Farwell once investigated? These are not the same question, and neither has an automatic answer. William Farwell, Matthew’s twin, testified under federal immunity. Former Stoughton deputy chief Robert Devine has contested an oversight board’s findings concerning the “Marty Riggs” Facebook account, saying he was hacked. Neither has been charged in Sandra’s death. Coffindaffer lays out what investigators would need: corroborated communications, authenticated account access, consistent timelines and proof of each person’s conduct. Knowing somebody i
Until a little under two weeks ago, Silicon Valley Bank was the sixteenth largest bank in the United States, the favoured choice of tech startups due to the tailored services it provided. But by 10th March 2023, American authorities were taking control of SVB following its collapse. It had assets of over $200bn, making for the second biggest bank failure in US history. There were a number of factors behind the collapse, and it’s causing concern as it’s common for one bank collapse to be followed by another, due to what’s called financial contagion. Indeed, just a few days later it was the turn of New York-based Signature Bank to collapse. And over in Europe, Switzerland’s second largest bank Crédit Suisse had to take out a $54bn to stay afloat, before then being bought out by the country’s largest bank UBS, in a bid to halt the crisis. Why did Silicon Valley Bank collapse? How do stock market crashes happen? In under 3 minutes, we answer your questions! To listen to the last episodes,
**SOCIAL SECURITY BEFORE AGE 62? YES! YOU COULD QUALIFY AT 43, 53, 60, OR EVEN YOUNGER!** Think you have to wait until age 62 to start receiving Social Security benefits? **Think again!** Millions of Americans know about Social Security retirement benefits, but many don't realize that certain people can receive monthly Social Security payments years, or even decades, before reaching retirement age. Need help with Medicare? Contact our friends at Chapter Medicare for FREE HELP!! 352-841-0632 **Could YOU qualify for Social Security benefits earlier than you think?** In today's video, **Dr. Ed Weir, a former Social Security Administration District Manager**, explains the often-overlooked Social Security rules that allow certain individuals to qualify for benefits in their 40s, 50s, and even younger. You may be surprised by who's eligible, which benefits are available, and what circumstances could allow you to start receiving payments. **IN THIS VIDEO, WE'LL ANSWER:** Can you really start
First up, we have a technical segment on how to setup Waydroid and Mitmproxy for good and evil, then in the security news: In the security news this week: ARTEX: pentesting goes AI If everything’s urgent, nothing is Disclosure clocks just got shorter NGINX, Apache and Java, meet RCE Who’s actually hacking with AI? Refrigeration with a root problem Old USB, new infections Router trouble grounds flights Fridge controllers need better defenses SANSAR uses your GPU and hides Vulnerability volume keeps climbing AI puts defenders to the test Taiwanese calls, intercepted Air traffic gets an AI copilot ESP32 wants a desktop Script tags, now serving skimmers Japan’s supercomputer goes offline Surveillance, courtesy of ad tech Cloud hosts peek inside protected VMs LLMs can edit their own brains France puts DNS on trial Leaked keys vanish in seconds Flipper One levels up Visit https://www.securityweekly.com/psw for all the latest episodes! Show Notes: https://securityweekly.com/psw-953
As artificial intelligence dominates boardroom agendas and vendor pitches, security leaders face immense pressure to rapidly adopt emerging technologies while defending against AI-powered threats. This rush toward innovation often leads organizations to chase shiny new tools at the expense of core cyber hygiene, creating dangerous blind spots in governance, visibility, and basic risk management. Gary Brickhouse, CISO at GuidePoint Security, joins Business Security Weekly to discuss as AI gets hired, security fundamentals don't retire. Gary cuts through the noise to examine why foundational security principles remain the true bedrock of enterprise resilience. Drawing on his dual perspective leading internal security architecture and advising clients on governance, risk, and compliance (GRC), Gary explores how security teams can balance executive demands for AI enablement without abandoning proven defensive practices. In the leadership and communications segment, CISOs Must Address Three
Interview with Douglas Day and Michiel Prins AI Is Not Killing Bug Bounty: It Is Raising the Bar AI is making it easier for more people to attempt vulnerability research, but Douglas’ experience shows that the biggest gains are going to researchers who already know how to find meaningful bugs. For elite security researchers, AI is not a replacement; it is a force multiplier. There is growing concern that AI will either replace security researchers or flood bug bounty programs with poor-quality reports. Douglas and Michiel can offer a more balanced view: AI can help experienced researchers scale their instincts, but it does not replace the judgment, context and impact assessment that make a report valuable. Topic Segment: Can an AI agent ever truly have an identity? (from Mike Privette's Security, Funded (https://www.returnonsecurity.com/t/newsletter) Newsletter) 60% - Yes, and it can be separate from humans 10% - Yes, but it only assumes the identity it runs under 10% - Yes, by use of
People directly affected by a local change should have more influence than other residents.
Share your view, then see how readers voted. No sign-in required. This poll is shared across stories.
Do you agree or disagree?
Common Quandary
A Common Quandary to discuss
Another conversation to explore, separate from this news story.
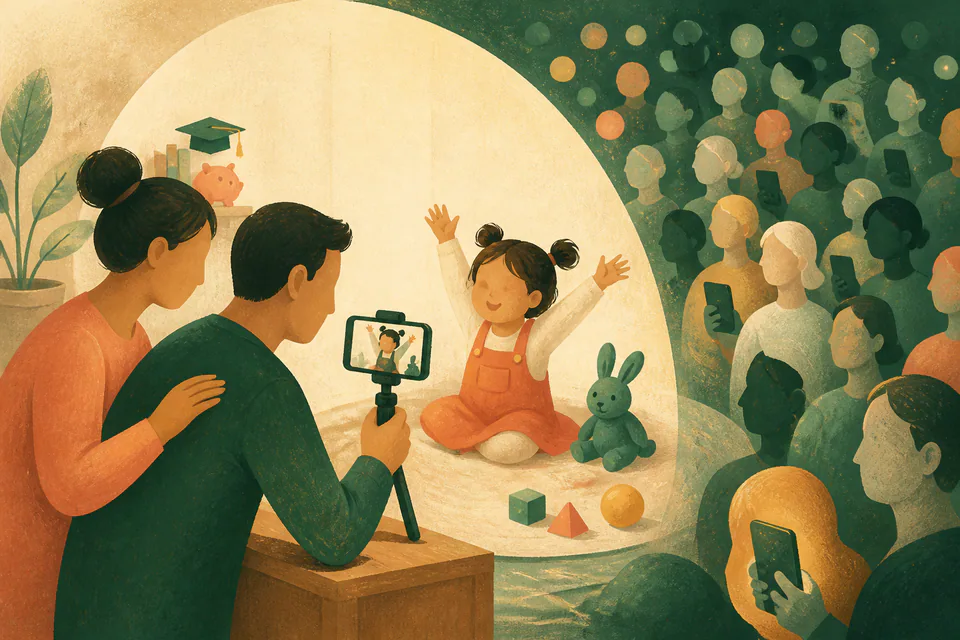
Your adorable child could pay for college by becoming an influencer. Do you start filming?
Parents post cheerful videos of their young child and earn enough to fund the child's education. The child enjoys filming now but cannot understand what it means for strangers to watch those moments years later.
Can parents consent to a permanent public identity on a child's behalf?