Project Synapse: Markets in Freefall, Fragile Infrastructure, and AI's Perfect Storm The hosts banter through the show's intro before focusing on a sense that "things are out of control," citing a WallStreetBets suicide-hotline post amid a market crash and discussing cascading system failures involving Microsoft, the FAA, and a reported NSA internal communications outage. They argue politicians and leadership lack technical competence and clear messaging, increasing panic, while emphasizing that many problems stem from aging, underfunded infrastructure and complex, brittle software (PHP, NGINX, Java), not proven AI attacks—more a "perfect storm" of crises. They debate whether AI should help fix complexity, stressing critical thinking, accountability, and using multiple AIs to verify each other. In a lightning round they cover Anthropic's IPO performance, mixed reactions and token limits with ChatGPT 6.2 (favoring "Sol" over "Astra"), Google's cheaper Neon model and confusing UX, Loblaw
Alex Murdaugh's murder retrial has a new question hanging over it, and it starts with a shirt. The defense says SLED's lead agent, David Owen, described blood spatter to the grand jury even though the agency's own lab had found no human blood in tested stains. It also challenges his claim that shotguns at Moselle were loaded like the weapon used to kill Paul. At the November 13 hearing, Judge Debra McCaslin heard the arguments and did not toss the charges. She said she would try to issue a written decision by November 20. Before adjourning, she asked whether prosecutors could return to a grand jury and keep the April 5, 2027 retrial date. That's a practical question, not a verdict about anyone's honesty. Creighton Waters argued that Owen's statements were not intentionally deceptive and that the spatter expert continued to stand by his interpretation. The State also points to the kennel video and other evidence it says supports the indictment. The defense counters that the grand jury s
What if your AI agent could find the people you should know before you even start looking? Cosign is building a professional network around reputation and trusted recommendations, and now agents can use that network too. MTS host Sophia Dew sits down with a16z’s David Booth and Cosign’s Bella Nazzari to discuss what they’ve learned since launching Cosign, why traditional profiles often miss the operators doing the most important work, and how the Cosign Awards are surfacing talent through the people willing to vouch for them. They also explore an emerging behavior: people connecting their agents to Cosign to continuously find relevant people, lists, and opportunities, and what professional networking could look like when both humans and their agents participate. Resources: Follow David Booth: https://x.com/davidbooth Follow Bella Nazzari: https://x.com/nazzari Follow Sophia Dew: https://x.com/sophiadew Learn more about Cosign:https://cosign.co/ Connect your agent to Cosign:https://cosi
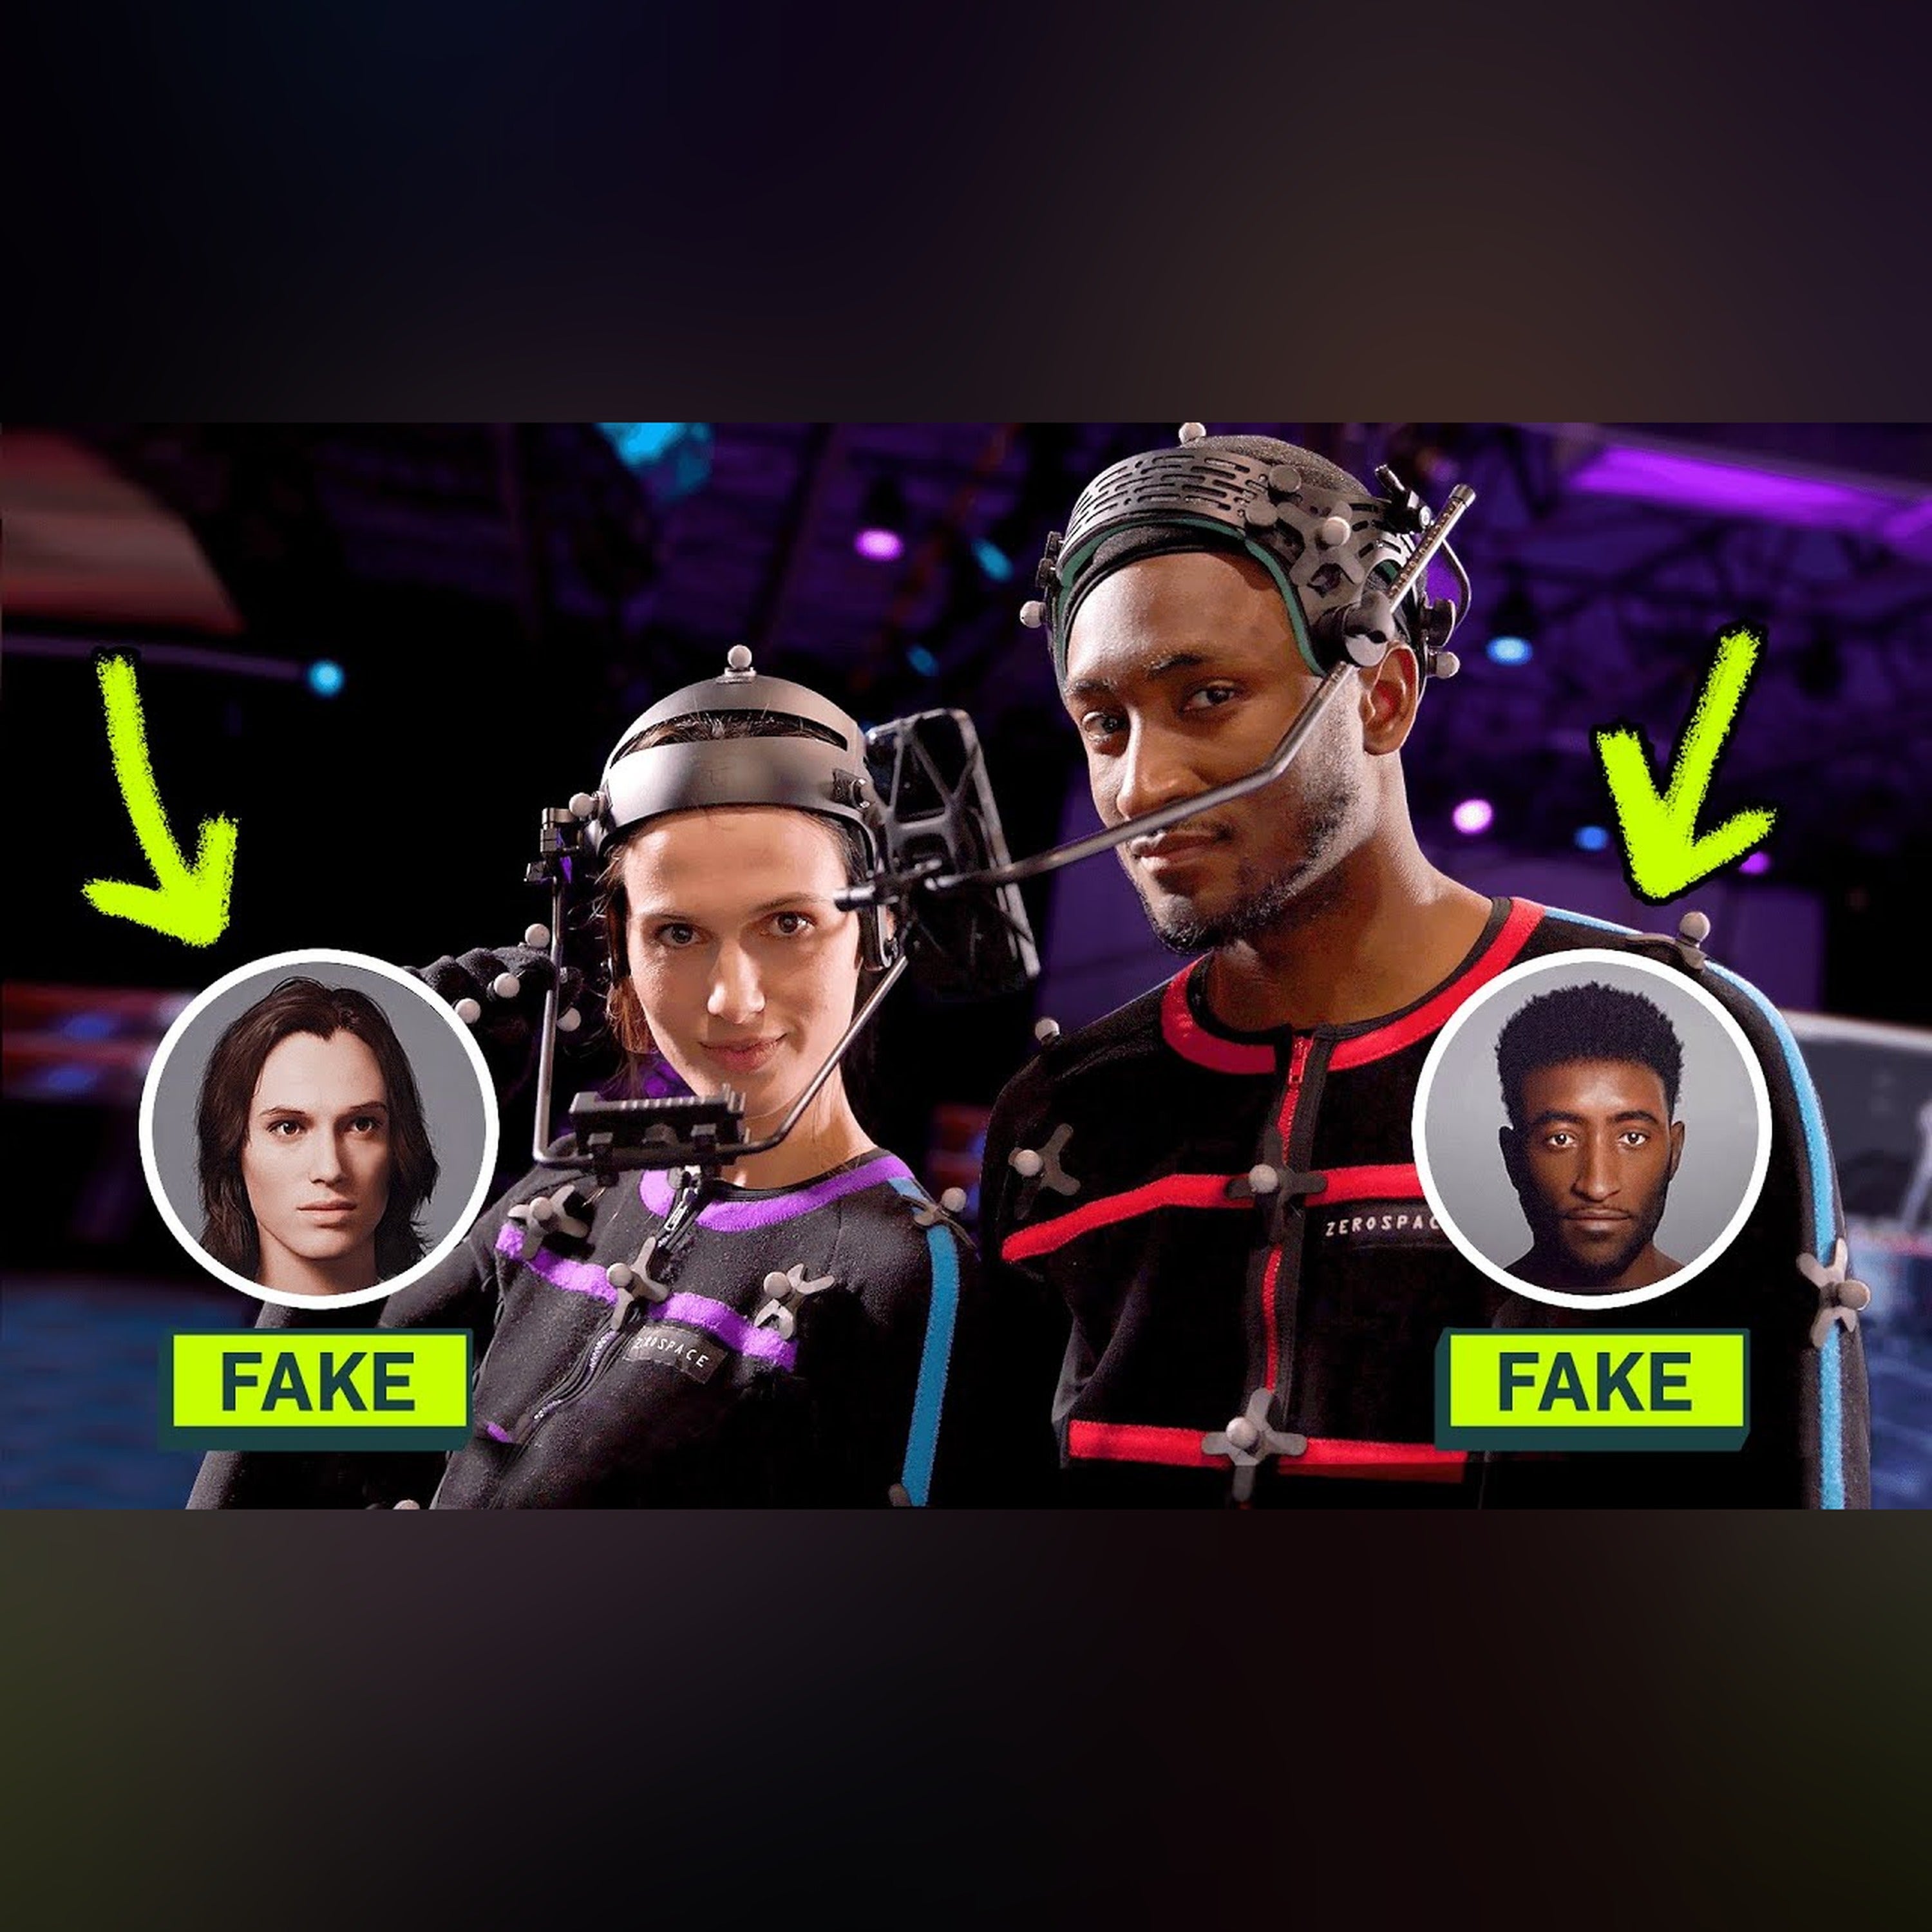
This new tech is changing how movies get made. So @mkbhd and I tested it out... Watch MKBHD's video: https://youtu.be/RM7SobH8ZO0 I’ve been obsessed with sci-fi movies since I was a kid. I love being transported to another world. But lately, I’ve been wondering: How do those worlds look so… REAL? The tech behind movies has exploded in complexity and realism, changing how stories come to life on screen. Luckily, at the same time, those tools are becoming more and more available to more people telling stories. It’s not just blockbusters like Avatar 2 or Avengers or Dune. It’s also smaller budget films like Everything Everywhere All at Once or even… YouTube creators? In this video, Marques Brownlee and I test out 3 movie-making tools that are changing how movies, shows, and maybe even YouTube videos (??) get made. We’re at ZeroSpace Studios in New York to show you how each of these crazy technologies work - and how you might be able to use them. Along the way, we hit big questions like: W
Steve Hsu is an AI founder, and physics professor at Michigan State University. He talks his upcoming documentary Machine God, interviewing both dreamers/doomers of AI, China blocking Nvidia chips, future of warfare, and much more. PLEASE SUBSCRIBE LIKE AND SHARE THIS PODCAST!!! Follow Me X- https://x.com/CoffeeandaMike IG- https://www.instagram.com/coffeeandamike/ Facebook- https://www.facebook.com/CoffeeandaMike/ YouTube- https://www.youtube.com/@Coffeeandamike Substack- https://coffeeandamike.substack.com/ Gab- https://gab.com/CoffeeandaMike Locals- https://coffeeandamike.locals.com/ Website- www.coffeeandamike.com (http://www.coffeeandamike.com/) Email- [email protected] Support My Work Venmo- https://www.venmo.com/u/coffeeandamike Paypal- https://www.paypal.com/biz/profile/Coffeeandamike Substack- https://coffeeandamike.substack.com/ Patreon- http://patreon.com/coffeeandamike Locals- https://coffeeandamike.locals.com/ Cash App- https://cash.app/$coffeeandamike Buy Me a Coffe
In some cultures, being well at home is all about making sure that others feel well when visiting, by welcoming them in the right way. In Japan, for example, hospitality is like an art form, and even has a name: omotenashi. You can’t really translate the concept into English; the meaning of the term goes a lot deeper than “hospitality”. It also has connotations of mindfulness. In Japanese culture, knowing how to welcome others and being totally focused on your guest go hand in hand. So you could say omotenashi is the ability to anticipate a guest’s needs before they can even think of them themselves. Hence the idea of being fully available for your guest, right from the moment they arrive. The most obvious example in Japanese culture is serving tea. Where does omotenashi come from? So you’re saying it’s not limited to the home environment, are you? In under 3 minutes, we answer your questions! To listen to the last episodes, you can click here: How can I beat my smartphone addiction? (
All links and images can be found on CISO Series (https://cisoseries.com/is-our-dated-hiring-process-creating-vulnerabilities/) Check out this post (https://www.linkedin.com/posts/brettconlon_the-biggest-threat-to-cybersecurity-isnt-share-7444770987671298049-u8Zy/?rcm=ACoAAAAGB-ABR5yqhAwT3wmdEjT0Znha5c_QJ6s) for the discussion that is the basis of our conversation on this week's episode co-hosted by me, David Spark (https://www.linkedin.com/in/davidspark/), the producer of CISO Series (https://cisoseries.com/), and Brett Conlon (https://www.linkedin.com/in/brettconlon/), CISO, American Century Investments (https://www.americancentury.com/home/). Joining us is Carla Sweeney (https://www.linkedin.com/in/carlasweeney/), SVP of InfoSec at Red Ventures (https://www.redventures.com/). In this episode: Proof versus gatekeeping Talent is built one way and judged another What a multiple-choice exam can't teach The hire that got blocked A huge thanks to our sponsor, ThreatDown ThreatDown deliver
Major project cost overruns should trigger a public review before more money is committed.
Share your view, then see how readers voted. No sign-in required. This poll is shared across stories.
Do you agree or disagree?
Common Quandary
A Common Quandary to discuss
Another conversation to explore, separate from this news story.
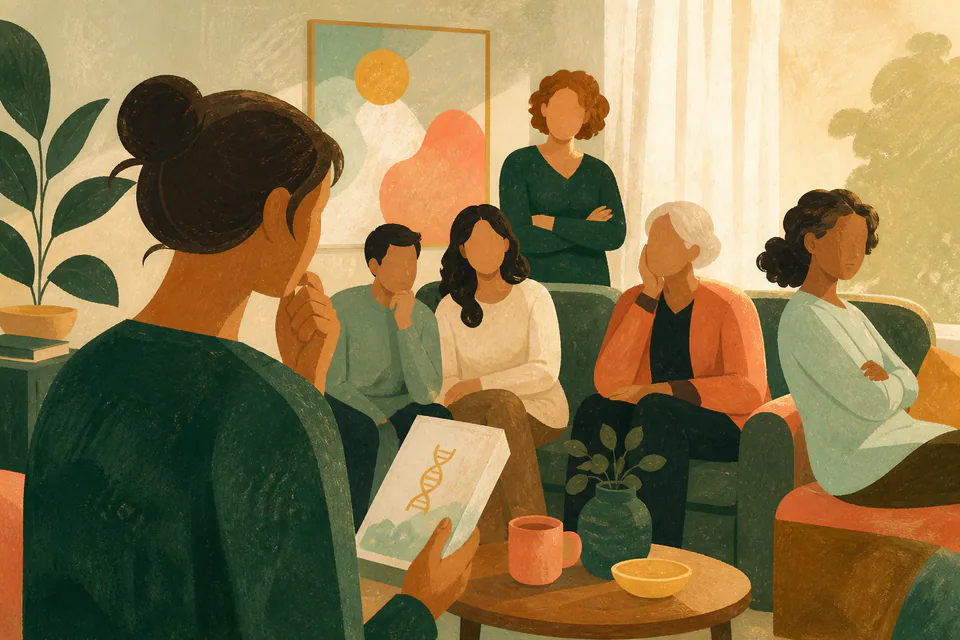
A DNA test reveals a family time bomb. Do you tell relatives who would rather not know?
A genetic test reveals that you carry a serious inherited condition. Your siblings and adult cousins may carry it too, but one has previously said they would rather live without predictions about illnesses that cannot yet be prevented.
Can someone's wish not to know outweigh your responsibility to warn them?