English-language podcasts

Security Weekly Podcast Network (Audio)

Holes In Everything, Even SSH - PSW #952

123 min

Listen through the publisher, then discuss the episode here or arrange an in-person Roundtable. Your city determines where to meet.

Roundtables are designed for groups of four, with a shared subject and room for everyone to speak. Come for discussion, with no dating expectation.

In the security news this week: SSH in Shambles Santa steals your podcast setup SAP’s double feature Terminal2Shell is CVSS 11 Dormant neurons, active backdoor Patched, but still exploitable 948 paths to root Barracuda serves root Node-RED, now with shell access The secret cigar recipe FBI agent, crypto thief Another AI agent identity mess 7.7 million reasons to care Reddit asks the breach question Who’s accountable when AI breaks? Espionage, chips, geopolitics Don’t ask again, leak forever AI catches cheating, flags everyone 1.4 million keys need revocation RSA, now with a countdown Fingerprint security, SD card reality Proving Signal’s machine code Thirty zero-days, one offline switch Visit https://www.securityweekly.com/psw for all the latest episodes! Show Notes: https://securityweekly.com/psw-952

Episode information is provided by the publisher. Listening takes place on the publisher’s service.

Listen at the source ↗

Featured places to meet in Palo Alto, CA

Explore these places and arrange a conversation through ThinkMatch.

City guide for Palo Alto, CA

More from Security Weekly Podcast Network (Audio)

Security Weekly Podcast Network (Audio)

MiTM Emulated Android Apps, Keep Calm And Carry On - PSW #953

117 min

First up, we have a technical segment on how to setup Waydroid and Mitmproxy for good and evil, then in the security news: In the security news this week: ARTEX: pentesting goes AI If everything’s urgent, nothing is Disclosure clocks just got shorter NGINX, Apache and Java, meet RCE Who’s actually hacking with AI? Refrigeration with a root problem Old USB, new infections Router trouble grounds flights Fridge controllers need better defenses SANSAR uses your GPU and hides Vulnerability volume keeps climbing AI puts defenders to the test Taiwanese calls, intercepted Air traffic gets an AI copilot ESP32 wants a desktop Script tags, now serving skimmers Japan’s supercomputer goes offline Surveillance, courtesy of ad tech Cloud hosts peek inside protected VMs LLMs can edit their own brains France puts DNS on trial Leaked keys vanish in seconds Flipper One levels up Visit https://www.securityweekly.com/psw for all the latest episodes! Show Notes: https://securityweekly.com/psw-953

Discuss this episode

Security Weekly Podcast Network (Audio)

AI Gets Hired, But Security Fundamentals Don't Retire and CIOs Need To Work w/ CISOs - Gary Brickhouse - BSW #474

57 min

As artificial intelligence dominates boardroom agendas and vendor pitches, security leaders face immense pressure to rapidly adopt emerging technologies while defending against AI-powered threats. This rush toward innovation often leads organizations to chase shiny new tools at the expense of core cyber hygiene, creating dangerous blind spots in governance, visibility, and basic risk management. Gary Brickhouse, CISO at GuidePoint Security, joins Business Security Weekly to discuss as AI gets hired, security fundamentals don't retire. Gary cuts through the noise to examine why foundational security principles remain the true bedrock of enterprise resilience. Drawing on his dual perspective leading internal security architecture and advising clients on governance, risk, and compliance (GRC), Gary explores how security teams can balance executive demands for AI enablement without abandoning proven defensive practices. In the leadership and communications segment, CISOs Must Address Three

Discuss this episode

Security Weekly Podcast Network (Audio)

Zero Trust Basics for Complex Modern Systems - Rob Allen - ASW #409

66 min

Orgs don't have to wait for the next zero-day, the next batch of 1,000 CVEs, or the next exploit in the wild to harden their defenses. Rob Allen talks about turning an expectation of "assume breach" into proactive defenses based on zero trust. We also discuss why "assume breach" doesn't have to be a pessimistic stance or even one that presumes malicious intent. After all, with so many agents being adopted throughout an org, restricting access and adding observability reduces the side-effects of agents taking actions you didn't expect regardless of what they were prompted to do. This segment is sponsored by ThreatLocker. Visit https://securityweekly.com/threatlocker to learn more about them! Visit https://www.securityweekly.com/asw for all the latest episodes! Show Notes: https://securityweekly.com/asw-409

Discuss this episode

Community Poll

Major sporting events should offer ways for people with limited budgets to take part.

Share your view, then see how readers voted. No sign-in required. This poll is shared across stories.

Do you agree or disagree?

Choose one answer

Common Quandary

A Common Quandary to discuss

Another conversation to explore, separate from this news story.

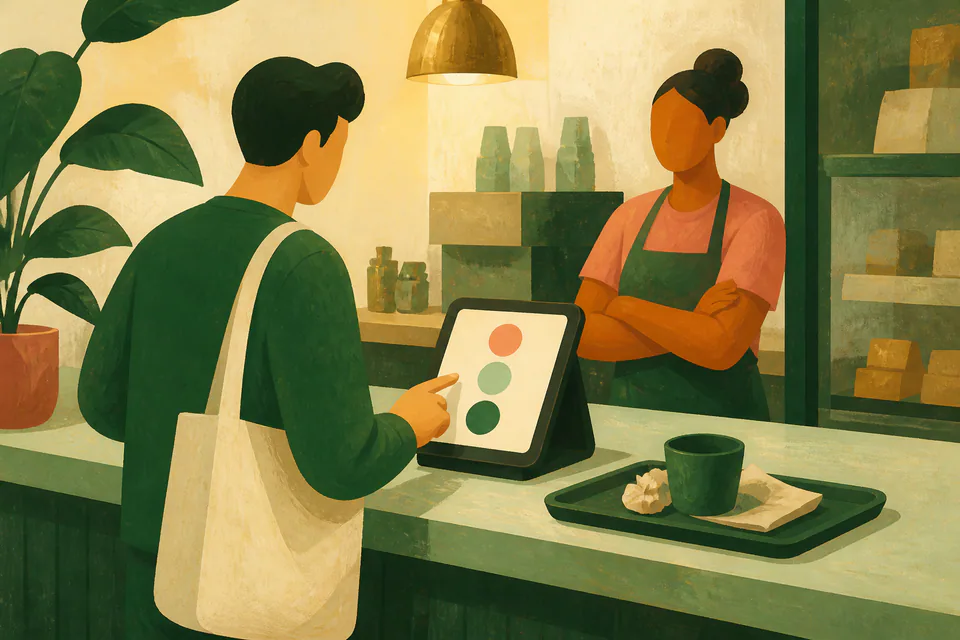
The touchscreen asks for a 25% tip while the cashier watches. What do you press?

At a counter-service shop, you place your own order, collect it, and clear the table. The payment screen suggests a twenty-five percent tip while an employee watches you choose.

When does a voluntary custom become an unfair social demand?

Explore this quandary